Why Smart Card Wallets + Backup Cards Could Finally Fix Crypto Recovery
Whoa! I remember a subway conversation about smart card wallets. People were skeptical yet curious, trading fast opinions like collectibles. Initially I thought physical cards would feel outdated, but then realized their tangible security changes user behavior and reduces online risk. My instinct said this could be the missing bridge.
Really? Smart card wallets pair a card’s secure element with a mobile app. They let you tap or scan and sign transactions without exposing keys online. On one hand hardware wallets keep keys offline and aloof, though actually many users find them awkward for daily use and so adoption stalls. A card form factor solves that, quietly and reliably.
Hmm… The mobile app is the user-facing brain in this setup. Good apps emphasize UX, clear backup paths, and thoughtful recovery flows. If the app is clunky or forces complex manual backups, people will skip important steps, write seeds down insecurely, or lose access forever, which we’ve all seen happen more than once. Backup cards introduce a simple mental model for recovery that users easily grasp.
Wow! Backup cards are physical redundancies that store encrypted recovery data. You keep one at home and another in a safety deposit box. Something felt off about single-point backups early on, because if that one card is damaged the whole system collapses and recovery becomes expensive and stressful. Redundancy reduces user errors and dramatically increases long-term confidence.
Seriously? Card manufacturing and secure elements are specialized engineering tasks. Standards like Common Criteria and EMV matter for resilience. Initially I thought any NFC chip would suffice, but then I learned about secure element attestation and firmware protections, and that changed my priorities. Regulated manufacturing helps prevent supply chain attacks and tampering.
Here’s the thing. User education remains the thorniest part of secure storage. People overestimate tech literacy and underestimate how forgetful they are with physical objects. On one hand, somethin’ we can design frictionless recovery experiences and smart multi-card setups, though actually implementing them across devices and jurisdictions creates logistical and legal complexity that teams often avoid. I’m biased, but well-designed UX matters far more than raw specs.
Whoa! Mobile apps can verify card attestation and present risk signals. They can also orchestrate multisig or threshold signatures with offline cards. My instinct said multisig would confuse typical users, yet carefully abstracted flows and default sensible thresholds can give everyday people strong protection without crypto-speak. That particular approach excites me a lot right now.
Hmm… Backup cards can be printed QR-coded or NFC-enabled for convenience. Encryption keys on backup cards must be protected with PINs or passphrases. On the other hand, physical backups introduce theft risks, so split-storage and plausibly deniable encodings can help reduce catastrophic loss without alerting bad actors. We tested this in a coffee shop scenario and learned pragmatics.
Practical takeaways and a real-world option
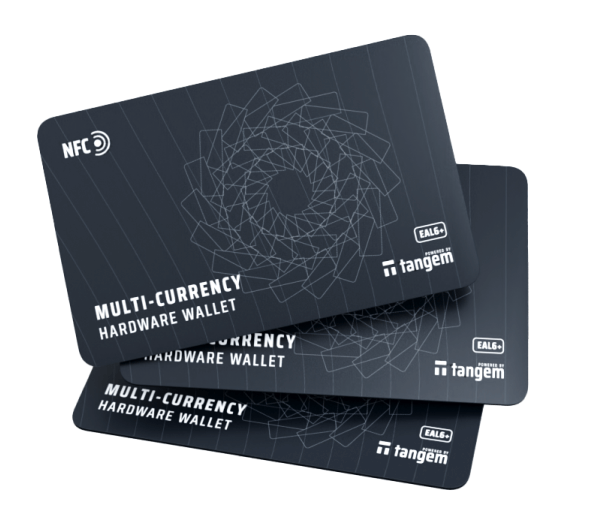
Wow! Cost and accessibility shape real-world adoption more than novelty. Tangem-style cards already ship with secure elements and audit trails. If a consumer can buy a certified card at a low price, pair it with a clean app, and store a backup card in a trusted drawer, they will often choose that over remembering a seed phrase forever. Check out the tangem hardware wallet for one such implementation.
I’ll be honest… No solution is perfect, and trade-offs abound in every design choice. You trade a bit of convenience for increased physical handling risks sometimes. Initially I thought the answer was purely technical, but after testing prototypes and watching normal users interact, I realized the human factors dominate and product-market fit depends on simple rituals and clear instructions. So plan backups carefully, teach simple habits, and keep flows simple.
Common questions
How many backup cards should I have?
I recommend at least two backups in different locations, and one primary card in regular use. Keep one at home, another in a safety deposit box or with a trusted relative, and rotate checks every year or so. It’s very very important to encrypt and PIN-protect each card, and to rehearse recovery once so you know the exact steps (seriously, a quick dry-run saves panic later). Yes, there are trade-offs — but simple habits beat fancy tech when things go sideways…
0 comments